
Security Brief
CISA’s latest KEV update puts two actively exploited vulnerabilities on a three-day patch clock, making exposed development tools and remote-access infrastructure a crucial priority. On Thursday, October 29, CISA added both flaws to its Known Exploited Vulnerabilities catalog, with federal agencies required to remediate them by November 1. For small businesses, the message is straightforward: forgotten internet-facing systems can become urgent business risks fast.
GitLab flaw CVE-2026-97229 carries a CVSS score of 10.0. An integer overflow or wraparound vulnerability affects GitLab Community Edition and Enterprise Edition. An unauthenticated attacker can execute arbitrary code on a GitLab server by sending a specially crafted regular expression in a CI/CD configuration, taking advantage of insufficient regex validation.
The KEV addition relates to an incident disclosed by Alpine Linux. An unknown threat actor tried to exploit Alpine’s GitLab instance on October 20 and 21 by sending crafted CI configurations that crashed GitLab worker processes eight times. In four of those crashes, the exploit failed at the next step. The attacker also downloaded Alpine’s GitLab container image. Later attempts on October 25 and 26 were blocked.
Alpine maintainers said, “The attack came close to working.” They found no evidence that the attack succeeded, but could not rule it out, so they treated the instance as compromised and rebuilt it from scratch. Checks showed that the aports repository, packages, and October 21 releases were not tampered with. The incident is a useful reminder that a self-hosted GitLab server or CI runner can hold source code and deployment secrets while sitting outside the everyday patching routine. If one is running in the environment, patch it now or take it off the internet.
Cisco flaw CVE-2026-76418 carries a CVSS score of 8.6. It affects Cisco Secure Firewall ASA Software and Secure Firewall Threat Defense (FTD) Software. An unchecked return value can lead to a NULL pointer dereference, allowing an unauthenticated remote attacker to make the device reload unexpectedly and cause a denial-of-service condition.
Cisco became aware of active exploitation earlier this month. It has not publicly identified the attackers, the number of targeted organizations, or what attackers did after gaining initial access. This is the second exploited Cisco firewall VPN zero-day since August. There is no official workaround; until patching, Cisco recommends disabling secondary authentication in affected tunnel groups.
A firewall that repeatedly reboots may not be breached, but the business impact can still be immediate. A VPN that cannot stay online can stop remote work just as effectively as a compromised one. The three-day KEV deadline is a strong reminder that automated exploitation can move quickly, and availability belongs in the security conversation too.
For help checking patch status or reviewing VPN and firewall concerns, Network Repair1 offers remote IT support and guidance.
Desk Upgrade: HP OmniBook X Flip 14
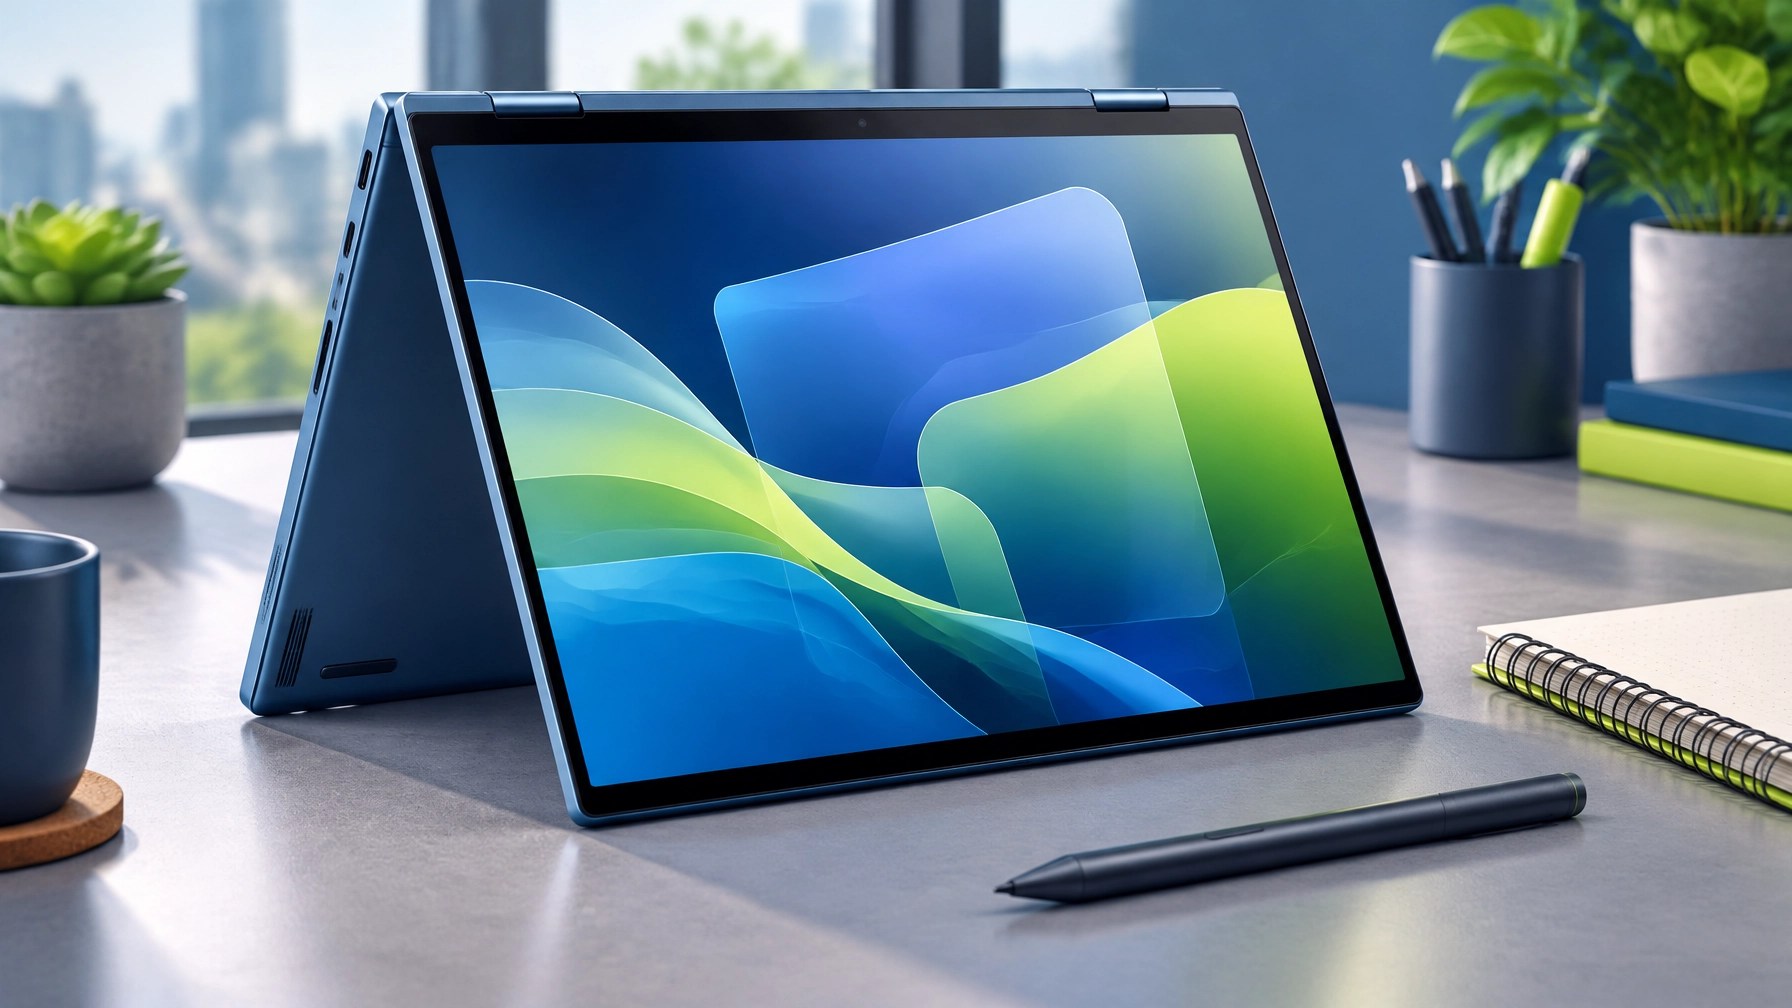
A versatile work machine does not need to come with a premium-price headache. The HP OmniBook X Flip 14 is listed at $649.99 at Best Buy, reduced from a $999.99 list price, a $350 or 35% discount as part of Best Buy’s Halloween Doorbuster sale. No retailer deep link here, just the price and the useful details.
The configuration pairs a 14-inch 2K (1920 x 1200) IPS touchscreen with an Intel Core Ultra 5 226V processor, 16GB LPDDR5 RAM, and a 512GB SSD. The processor supports up to 40 NPU TOPS for AI tasks, and the laptop includes Copilot+ PC features. Its all-metal 2-in-1 design comes in Atmospheric Blue, while the battery is described as comfortably lasting a workday.
TechRadar reports that its Tom’s Guide sister site tested this exact configuration, describing it as a premium, durable convertible with a solid display and strong mid-range performance. That test recorded more than eight and a half hours of battery life. The flexible design makes it a fit for students and professionals who want one device for work, note-taking, and entertainment.
There are caveats. The laptop comes loaded with bloatware that buyers may want to remove, the gapless keyboard takes some getting used to, and the chassis warms up under heavy loads. The price is good, but not the lowest seen: it regularly sells below list, and Tom’s Guide reviewed it when it was going for $599. It may drop further over Black Friday next month, so this is a worthwhile deal rather than an unbeatable one.
Daily Links
- The Hacker News: CISA adds actively exploited GitLab and Cisco flaws to KEV
- TechRadar: HP OmniBook X Flip 14 deal at Best Buy
Grow with Network Repair1
A big thank-you to our community: Network Repair1 has reached 13,000 YouTube subscribers and more than 1.1 million lifetime views. Every view, subscription, and share helps us keep creating useful technology coverage and practical content. We’re grateful to everyone growing with us.
Promote with Network Repair1
🚀 Shopify and Amazon product videos: Let’s showcase your products with clear, engaging content that can boost visibility and help your brand grow. Collaborate with us.
💻 Remote IT support: We can help with troubleshooting, patch checks, and VPN or firewall guidance. Get remote support.
🤝 Let’s collaborate: Together, we can create useful content and stronger technology experiences.
Don't settle for subpar tech. Grab the professional-grade gear we trust to keep our networks running fast and secure.
The items mentioned are featured on the YouTube channel.
📞 805-723-9608
Leave a Reply