
Security Brief
Ransomware groups are turning a familiar business tool into an unexpected entry point: the company VPN. CVE-2026-0257 is an authentication bypass affecting the GlobalProtect portal and gateway in Palo Alto Networks PAN-OS, as well as Prisma Access. The vulnerability stems from the way affected firewalls handle authentication override cookies, relying on them without sufficiently detailed validation and integrity checks. That can allow remote, unauthenticated attackers to forge a cookie and establish an unauthorized VPN session.
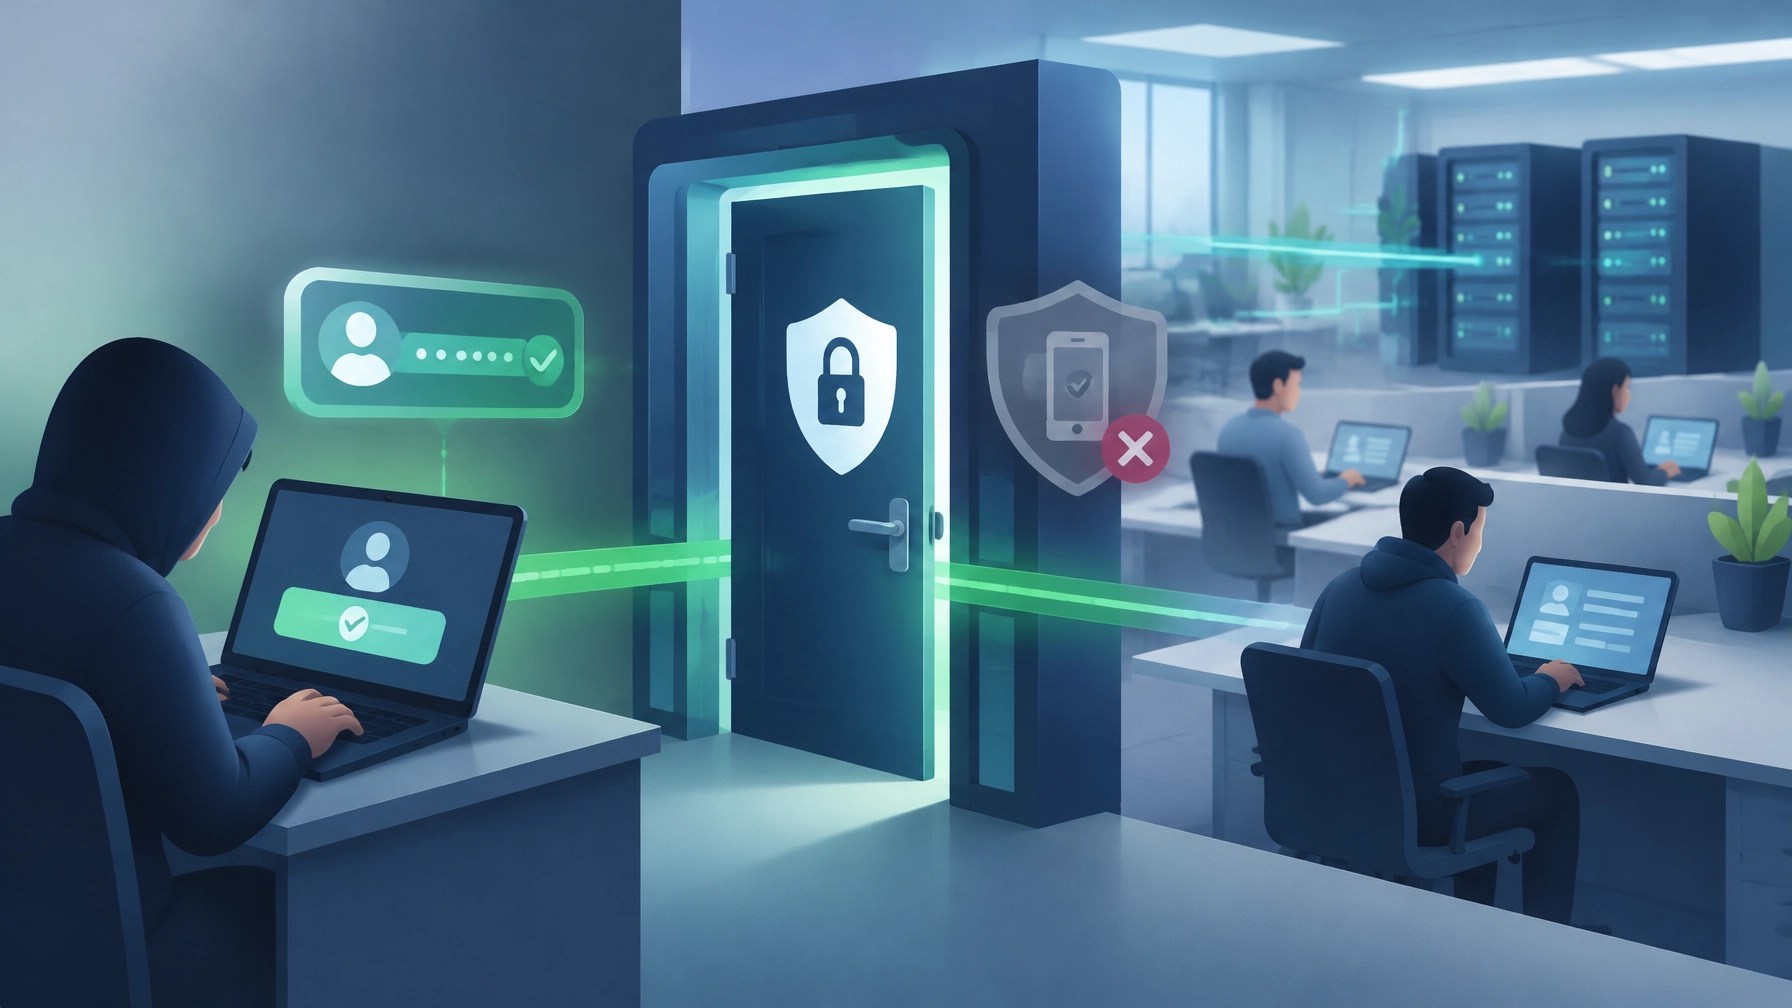
The flaw was patched in May 2026, but the patch did not make it disappear from attackers’ to-do lists. Help Net Security reported on October 21 that ransomware groups have exploited it since June. Unit 42 has named Qilin and Inc among the operators, while ReliaQuest has tracked activity associated with Qilin and Settra. In observed intrusions, attackers used the VPN access to establish sessions while bypassing MFA, then relied on legitimate IT management tools to move through networks. That’s the unnerving part: the activity can resemble ordinary remote work.
One Unit 42 investigation shows how far that initial foothold can reach. Attackers moved from a VPN gateway to vCenter, disabled ESXi security controls, then used a custom tool to extract credentials offline from a domain controller’s virtual disk. Because the credentials were accessed outside the running guest operating system, this approach bypassed in-guest EDR controls. Unit 42 also observed attackers chaining the initial access with older Veeam exploit activity involving CVE-2023-27532.
For a small business, the front-door analogy is more useful than the familiar “broken window” image. The intruder is not necessarily forcing a noisy way into the network; the intruder may be using your own VPN and blending in with your remote employees. ReliaQuest expects exploitation to continue over the next three months, so a prior patching reminder is not a reason to assume the risk has passed.
Administrators should upgrade affected deployments immediately, and disable authentication override cookies where they are not required. After patching, terminate all active GlobalProtect sessions: patching alone does not remove access established before remediation. Review unexpected connections and investigate suspicious hostnames, including “kali,” alongside other unusual VPN activity. Small businesses that depend on remote access can also benefit from keeping network configurations, endpoint protection, and user access practices under regular review. Network Repair1 provides remote IT support for troubleshooting, network diagnostics, system protection, and other technology needs; firewall remediation should be coordinated with the organization’s network administrator or provider.
Desk Upgrade
The Logitech MX Anywhere 3S is a compact wireless mouse designed for people who work from more than one place, or switch between more than one computer. TechRadar reported an Amazon price of $69.99, down from $89.99, a $20 discount. It has been seen as low as $60 before, though, so shoppers willing to wait may find a better price around Black Friday.
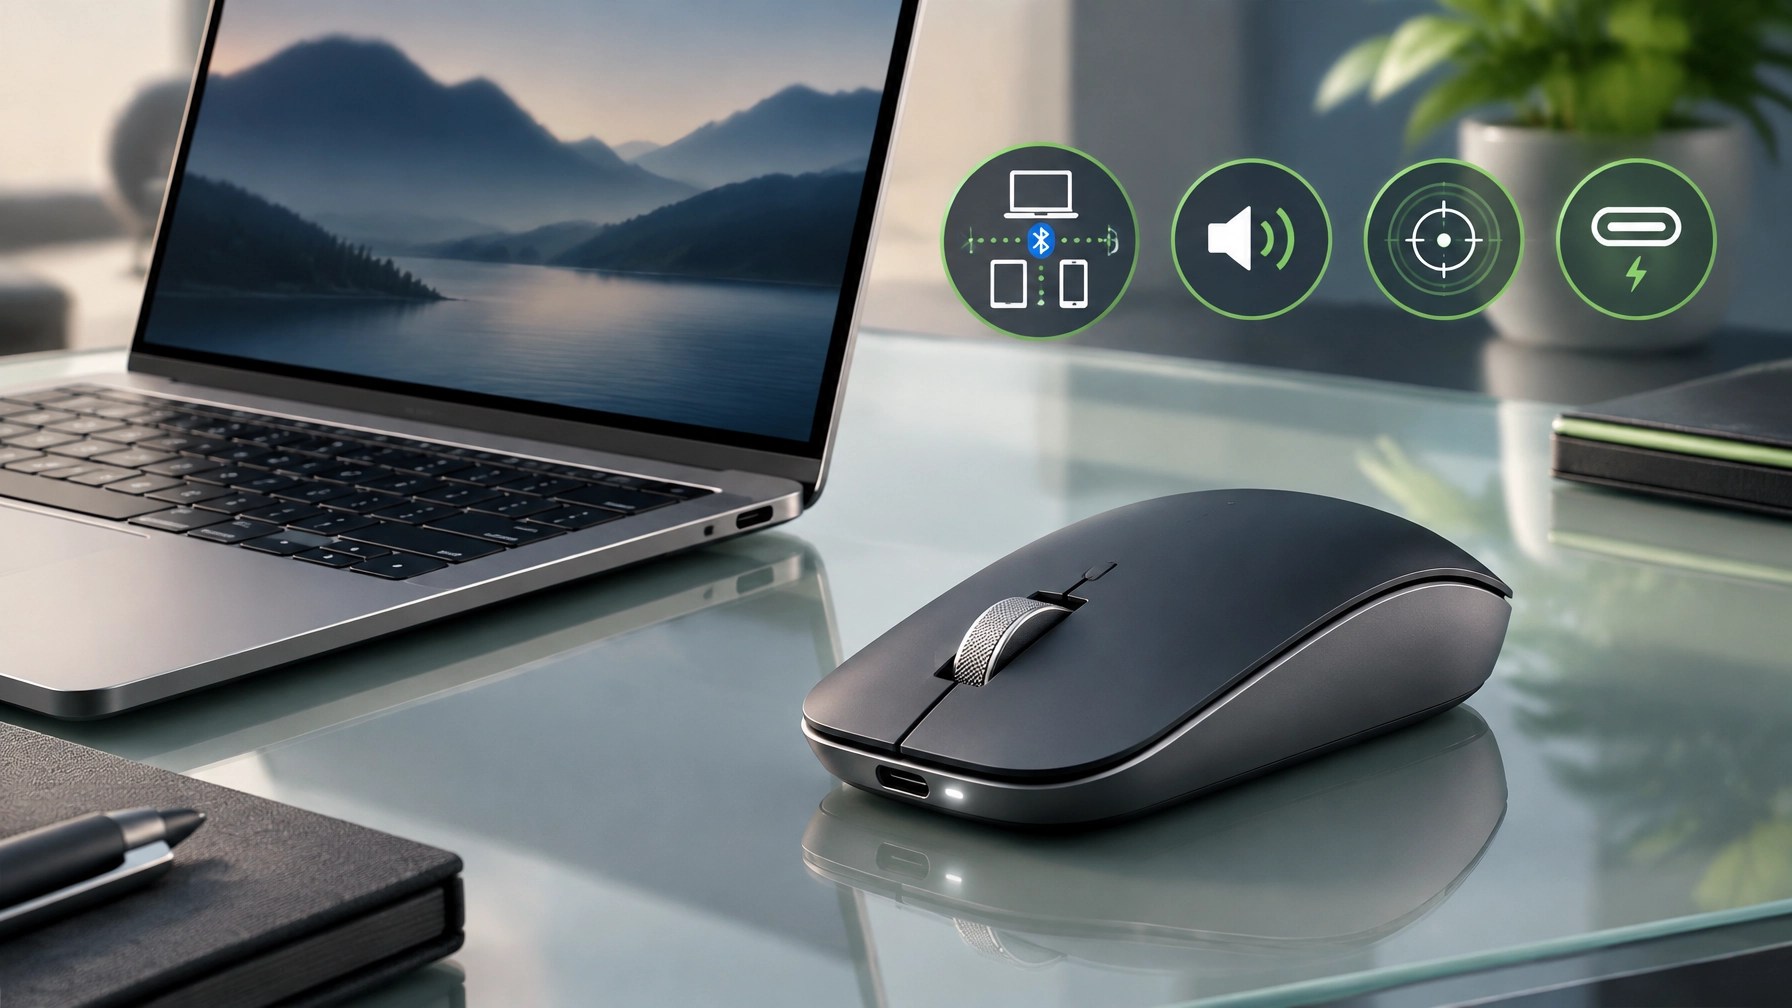
Its 8,000-DPI Darkfield sensor tracks on almost any surface, including glass at least 4mm thick. The MagSpeed electromagnetic scroll wheel can move through up to 1,000 lines per second, and a side button enables horizontal scrolling. Quiet Clicks keep the mouse from sounding like a tiny office percussion section, while six customizable buttons give users room to tailor common actions.
The MX Anywhere 3S pairs with up to three Bluetooth devices and supports quick switching between them. Logitech Options+ software adds app-specific profiles on Windows and macOS, and USB-C charging helps keep it ready for the next work session. Logitech rates battery life at up to 70 days on a full charge. At 99g and roughly 100mm long, it is portable without being a miniature novelty.
That combination makes it a strong fit for laptop owners, mobile professionals, and anyone who regularly moves between computers or work surfaces. The sensor and scrolling features can make daily work feel more controlled, while the compact size makes packing it simple. The honest caveat: if the mouse will only be used for basic web browsing, a less expensive model can do the job. At $69.99, this is a capable upgrade, but not necessarily the best deal for someone who does not need its extra features.
Daily Links
- Help Net Security: Ransomware gangs exploit Palo Alto GlobalProtect VPN flaw
- Unit 42: Active exploitation of PAN-OS CVE-2026-0257
- TechRadar: Logitech MX Anywhere 3S deal and review
- Logitech MX Anywhere 3S product page
Grow with Network Repair1
Network Repair1 has reached 13,000 YouTube subscribers and passed 1.1 million lifetime views. Those milestones reflect a growing community looking to us for practical technology coverage, product insights, and helpful digital content.
We’re grateful to everyone who watches, shares, and supports the channel. This audience and experience help us connect useful technology information with real people, and help businesses bring their products to a wider audience.
Promote with Network Repair1
- 🎥 Product videos: Let’s collaborate on engaging content for Shopify and Amazon sellers through our product video and sponsorship services.
- 💻 Remote IT support: We can help with troubleshooting, network diagnostics, and technology support through our remote services.
- 🤝 Let’s grow together: Call us at 805-723-9608 to discuss a project or support need.
Loved today's review? You can find this product and all our top picks on our official Amazon storefront.
The items mentioned are featured on the YouTube channel.
https://www.amazon.com/shop/networkrepair1?ref_=cm_sw_r_cp_ud_aipsfshop_XV0ER95A5EVVJDPA7W6A_1
Leave a Reply