
Welcome to Saturday’s roundup. Today’s security brief is about the online checkout that can look perfectly normal while an attacker works behind the scenes, and the desk upgrade is a comfortable pair of headphones now listed at a striking price.
Security Brief
The checkout page is the front door customers use most, but it can be the door owners inspect least. Sansec researchers report attackers are exploiting PolyShell, an unrestricted file-upload flaw in Adobe Commerce and Magento tracked as CVE-2026-48356, to breach hundreds of stores. The attackers can inject a malicious loader through a Magento CMS block, which then fetches and runs an attacker-controlled payload. Researchers have not recovered the next-stage malware, so the final objective remains unclear, but the campaign has reportedly been active since at least July 2025.
The other urgent item is CVE-2026-111497, a Brotli decoder memory-corruption flaw nicknamed Broccoli2Shell, HTTP2Shell and Node2Shell. CISA added it and PolyShell to its Known Exploited Vulnerabilities catalog on October 27. A crafted Brotli-compressed stream can corrupt memory, expose sensitive data, crash a process or potentially enable code execution. This is no longer just a lab concern: ELLIO says its sensors detected real exploitation attempts carrying the public exploit, and confirmed that the payload can open a shell on vulnerable builds.
Brotli’s reach makes the issue easy to overlook: it appears across runtimes and services including Node.js, PHP, Bun, .NET, Python, Envoy Proxy and Istio. Wiz estimates that 91% of cloud environments have resources vulnerable to CVE-2026-111497, and 82% have publicly exposed Node.js instances. For Node.js, fixed releases include 22.23.4, 24.22.1 and 26.12.1. PHP has emergency patches as well, and other projects have shipped their own fixes. Check the versions in use, including dependencies bundled inside applications and services. For the Brotli flaw, upgrading is the complete fix.
For store owners, apply Adobe’s APSB26-73 security update immediately, then review Magento CMS blocks for injected scripts, unexpected admin content and unfamiliar web shells. If the store runs Drupal Commerce Core, check for the separate actively exploited access-bypass flaw, CVE-2026-118539, and audit orders for inconsistencies. Drupal fixed it in Commerce Core 3.3.13 and 8.x-2.41; the module is used by more than 42,000 sites. Federal civilian agencies have until November 10 to patch the two CISA-listed flaws. That deadline is not a reason for other operators to wait. A checkout can look fine while a skimmer quietly copies card details, so patching and auditing beat hoping.
Desk Upgrade
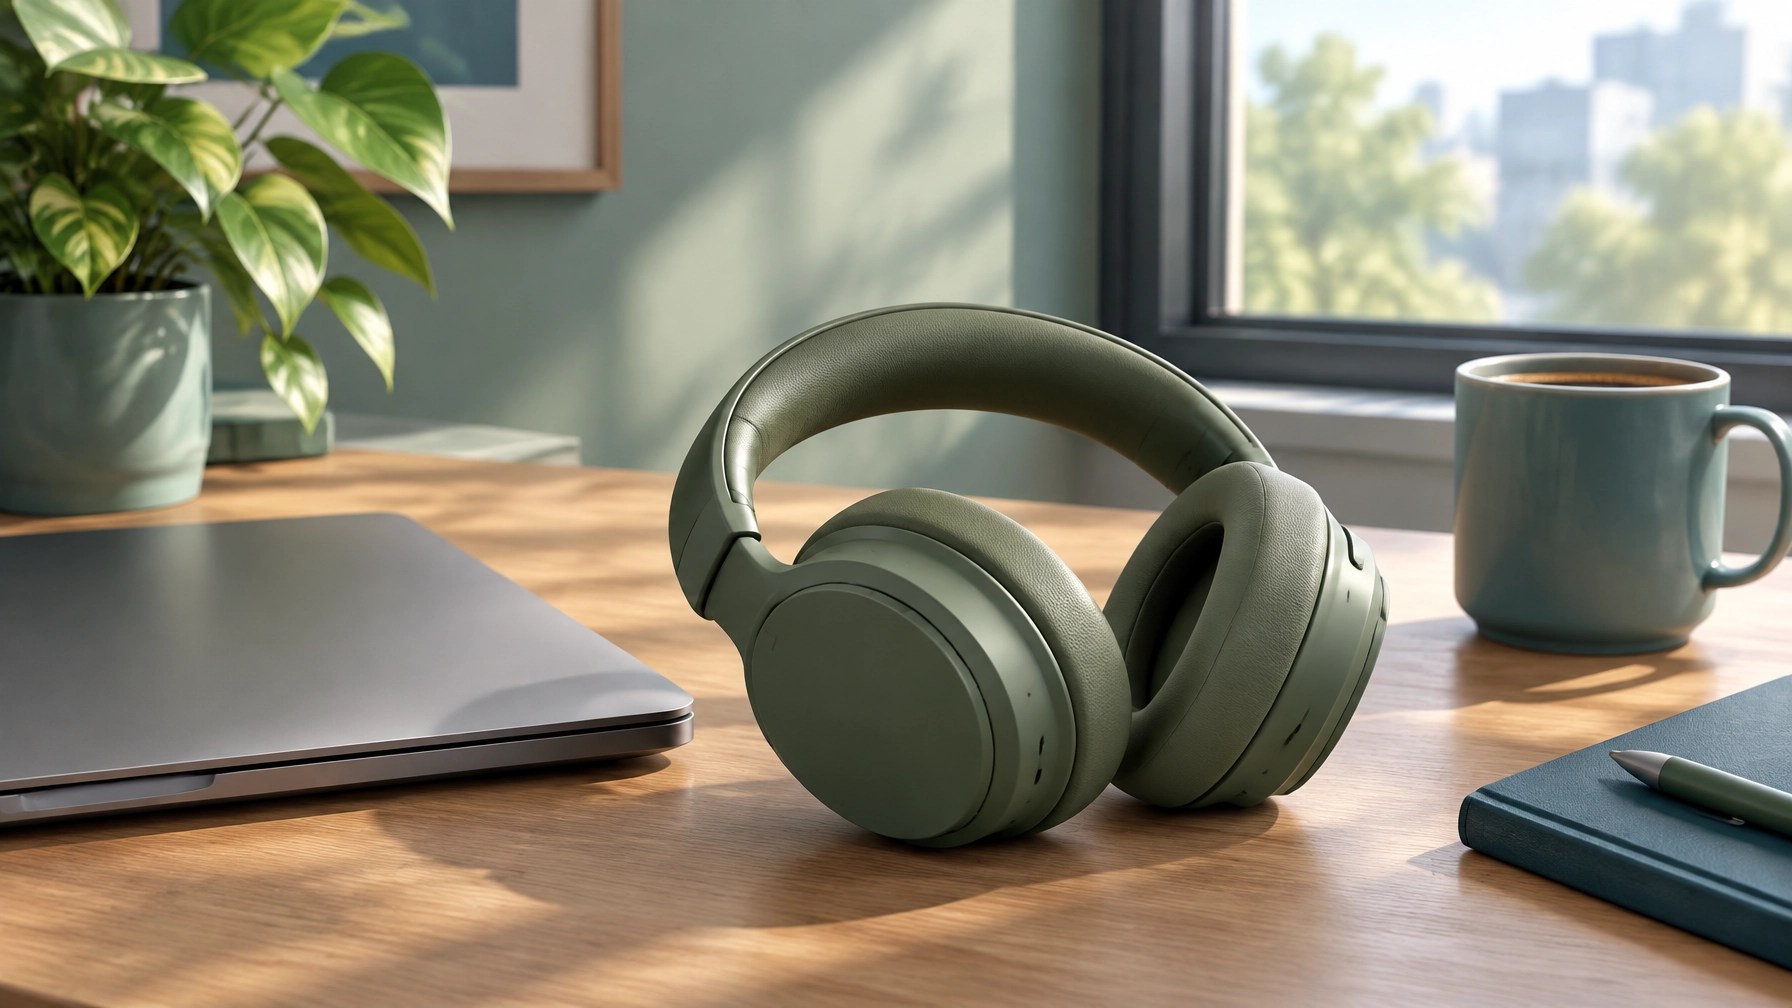
This Saturday’s desk pick is the first-generation Bose QuietComfort over-ear headphone, listed at $169, down from a $359 list price. The price was verified October 30 by Mereja.Tech and StackTheDeal, and Amazon’s listing shows the same price without a coupon. Cypress Green, Ice Blue, Moonlight Grey, Petal Pink and White Smoke were confirmed at $169, though other finishes may cost more. Switch colors on the listing and confirm the price before purchase, since deal pricing can change.
The appeal is focused and practical: Bose’s active noise cancellation, Quiet and Aware modes, adjustable EQ through the Bose app, and multipoint Bluetooth for two devices at once. Battery life is rated up to 24 hours, while a 15-minute charge can add about 2.5 hours of listening. USB-C charging keeps the setup current, and the included wired audio cable offers a useful fallback when the battery is depleted. At about 240 grams, the padded, plush fit is a particular draw for long work sessions and travel.
The trade-offs are worth knowing before checkout: there is no water-resistance rating, no automatic wear detection, and the headphones cannot be used while charging. Some users report occasional Bluetooth micro-stutters when using multipoint. For sound quality and extra features, Sony’s flagship models and Bose’s newer QuietComfort Ultra have the edge. Tom’s Guide has argued that the second-generation QuietComfort is a harder sell while the first generation is available at $169. At this price, the first-gen model makes a strong comfort-and-quiet pick for open offices, calls and travel, with a wired backup that can save the day when Bluetooth or battery power cannot.
Daily Links
Security Brief
- Adobe Commerce PolyShell attacks breach hundreds of stores as Brotli exploit traffic emerges, The Hacker News
- Adobe Commerce security update APSB26-73
- NVD entry for Brotli decoder flaw CVE-2026-111497
- Drupal warns of critical Commerce Core flaw exploited in attacks, BleepingComputer
- Drupal security advisory SA-CONTRIB-2026-254 for Commerce Core
Desk Upgrade
- Bose QuietComfort Headphones, Cypress Green, on Amazon
- TechRadar review of the Bose QuietComfort Headphones
- Tom’s Guide on the first-generation QuietComfort at $169
- Mereja.Tech’s October 30 deal roundup and price verification
Grow with Network Repair1
We’re celebrating 13,000 YouTube subscribers and 1.1M+ lifetime views across our channel and social platforms. Thank you for watching, sharing and growing with us. Subscribe to Network Repair1 on YouTube and follow along for practical tech guidance, product reviews and fresh content.
Promote with Network Repair1
- 🎬 Product videos that make listings pop: We create professional content for Shopify and Amazon sellers.
- 🔧 Remote IT support that keeps work moving: We troubleshoot computers and networks without an on-site visit. Explore our remote services.
- 🤝 Brand collaborations and content creation: Let’s collaborate and create meaningful product stories together.
- 📩 Ready to reach out: Connect with us through our collaboration page.
We've done the troubleshooting so you don't have to. Grab the gear and guidance that keep your setup running right, the first time.
The items mentioned are featured on the YouTube channel.
https://www.amazon.com/shop/networkrepair1?ref_=cm_sw_r_cp_ud_aipsfshop_XV0ER95A5EVVJDPA7W6A_1
805-723-9608
Leave a Reply