
Security Brief: Patch the PHP2Shell vulnerabilities
Treat web-facing PHP patching as crucial to keeping business websites available and protected. The PHP security team released emergency fixes on October 21 for two critical, unauthenticated remote code execution flaws, CVE-2026-109618 and CVE-2026-109619, known together as PHP2Shell. Discovered by researchers at Calif, OpenAI, and Wiz, the vulnerabilities affect PHP installations that serve web requests, including PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP, and LiteSpeed. Risk is highest with mod_php, where an unauthenticated request can trigger an attack before application code runs.
Both flaws relate to PHP memory becoming corrupted when a request ends abnormally, creating paths to code execution with the privileges of the web worker. This is not limited to businesses that manage their own code: PHP powers an estimated 75–80% of websites, including WordPress, Joomla, and Drupal sites. VirusTotal estimates more than 5.1 million PHP hosts are exposed online, roughly 3.8 million with at least one port open. Cloudflare deployed WAF rules and reported early attacks before patches were available; CISA urged immediate updates, while the UK NCSC advised organizations to update or take affected systems offline until they can patch.
Install a fixed release as soon as possible: PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35. PHP 8.1 and earlier no longer receive standard updates from the PHP project, so contact the Linux distribution or hosting provider about available backported fixes, or plan a move to a supported PHP version. The PHP team also supplied minimal source backports for PHP 7.4, 8.0, and 8.1. CISA’s October 23 alert said it had not observed successful exploitation at the time of publication, underscoring the importance of patching before a vulnerability becomes a confirmed incident.
Temporary configuration measures may reduce some exposure but do not replace the official fix. For CVE-2026-109618, PHP’s guidance includes setting memory_limit=-1 in a non-overridable server configuration, using a low post_max_size-8M without uploads or 32M when uploads are required, and applying container or cgroup limits. For CVE-2026-109619, the guidance includes setting session.upload_progress.enabled=0 and restarting workers; on PHP 8.5, fatal_error_backtraces=0 can block a confirmed path when workers are restarted. These are administrator-level controls, and the PHP team warns that mitigations do not fully protect systems.
For a small business, the practical first move is to ask the hosting provider which PHP version runs the website and whether the host has applied the PHP2Shell fix. Update WordPress core, plugins, and themes as part of routine maintenance, but do not confuse those updates with patching the PHP engine itself. If a provider will not confirm that the server is patched, or cannot explain its plan for an unsupported PHP version, treat that as a serious hosting concern and seek qualified assistance.
Desk Upgrade: UGREEN Nexode Smart Display power bank
For mobile work that depends on phones, tablets, or lightweight laptop use, the UGREEN Nexode 10,000mAh Smart Display power bank pairs portable power with useful status information. A deal reported by 9to5Toys on October 19 put the unit at $59.99 shipped, $20 below its usual $79.99 price and a new low at the time; a larger 20,000mAh version was listed at $75. Sale prices can change, so check the current offer and terms before purchasing.
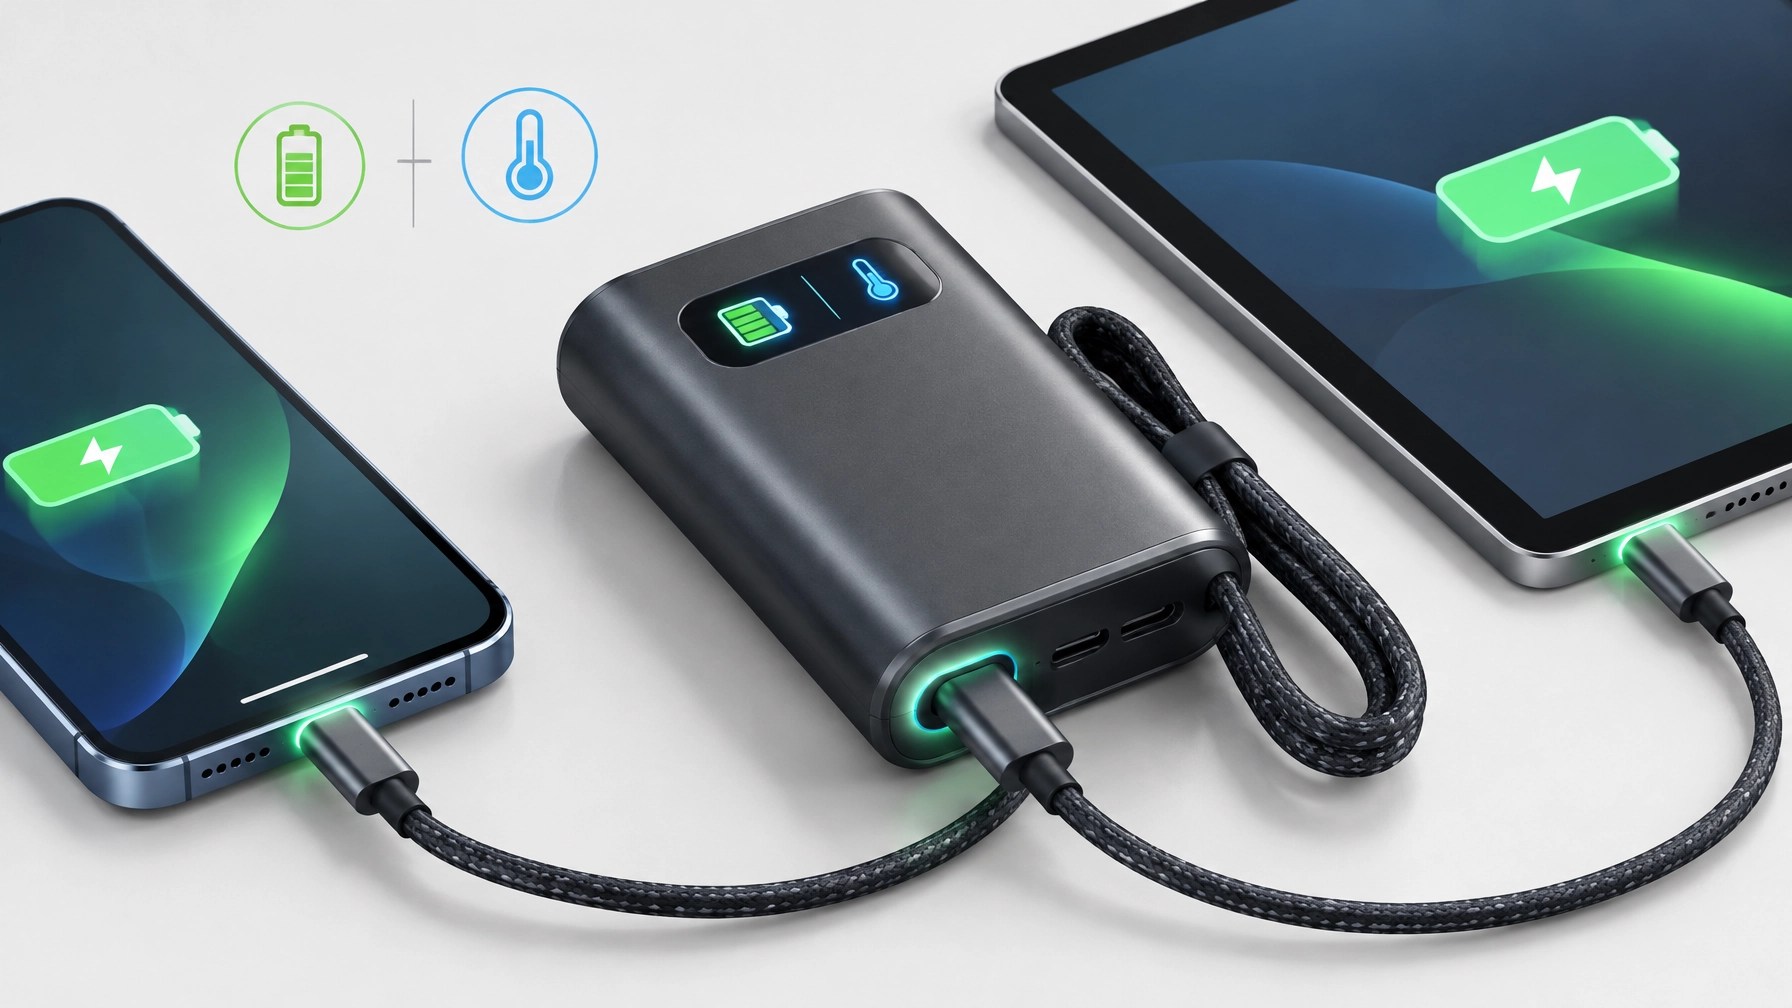
The 45W maximum output can serve phones, tablets, and some laptops, while a built-in 18cm braided USB-C cable works as a wrist strap and saves packing a separate cord. A USB-C port and USB-A port join the integrated cable to support charging three devices at once. The front display reports remaining battery, charging output, battery health, cycle counts, and temperature; its battery management system can also warn about abnormal, high, or low temperatures. That small diagnostic readout is especially useful for a power bank that spends time in a travel bag.
UGREEN lists 36W fast recharging, with a 0–100% refill taking about 2.3 hours. The unit weighs roughly 200g, has a compact, airline carry-on-friendly footprint, and the cited deal report says it can charge a Galaxy S25 Ultra to 65% or an iPhone 17 Pro Max to 66% in 30 minutes. Pass-through convenience makes it a useful companion for remote workers moving between client sites and shared workspaces, and for content creators filming product footage away from a studio.
Keep the capacity in perspective: 10,000mAh is in the one-full-phone-charge-plus class, not a multi-day laptop lifeline. The 45W ceiling can support many laptops while idle or under light use, but it is not designed to sustain demanding workloads. Compare that capacity and output with the devices and time away from an outlet before choosing a travel charger.
Daily Links
- PHP ships emergency patches for critical PHP2Shell flaws. BleepingComputer
- CISA alert: Critical vulnerabilities in PHP require immediate patching
- UGREEN power bank deal coverage: 9to5Toys
- UGREEN Nexode Pro power bank: official product page
Grow with Network Repair1
🎉 13,000 YouTube subscribers: Thank you for helping our community grow.
📈 Over 1.1 million lifetime views: Your support helps more people discover useful tech coverage.
▶️ YouTube
Promote with Network Repair1
🎥 Shopify and Amazon sellers: We create product videos and reviews to help showcase products, let’s collaborate and grow together.
💻 Remote IT support: We help individuals and small businesses troubleshoot, optimize, and stay connected through remote services.
📺 YouTube · 🎵 TikTok · 📸 Instagram · 📘 Facebook
📞 805-723-9608
Ready to upgrade your tech? Check out our curated list of essential tools to keep you connected and productive.
The items mentioned are featured on the YouTube channel.
Amazon Store
Leave a Reply